Showing posts with label security. Show all posts

Beware! Google adsense ads may embarrass you and finally may land you in legal hurdles too!

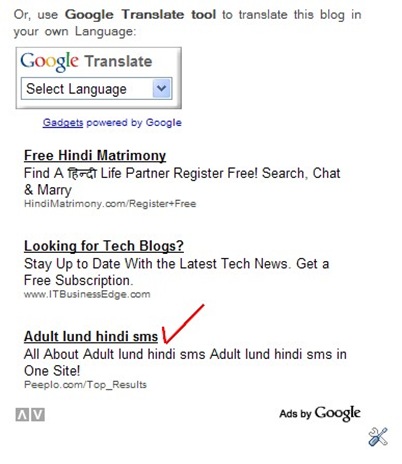
Recently, in one of my Indic blog, a Google Adsense appeard that is really embarrassing to both me and my readers.

Here is the screenshot of ads that appeared:

google adult ads

Apparently, the cunning advertiser had successfully fooled Google bot with Adult Hindi Keywords. I had immediately blocked the URL in Adsense ads filter, but by the time, damages had been done. Moreover, in India, displaying such advertisement in your blog may land you in serious legal hurdles and you may actually land in JAIL displaying such adult content on your blog!

Google must review its own advertisement policy and strict measure must be adopted to curb such menaces. A better solution – such as advertisement moderation is the need of the day.

In the meantime, be aware with your Google Adsense!

Now Phishers have started targeting innocent mobile phone users

After Internet, phishers have started targeting mobile phone users. They simply send a sms or mms message to contact them back either through a mobile number or through email. And when you get trapped in their hand, they extort money in the name of service charge, courier charges, taxes and what not. BEWARE of such messages and never reply them.

Here is an interesting story appeared in Fsecure blog:

There's an ongoing SMS / e-mail fraud underway.

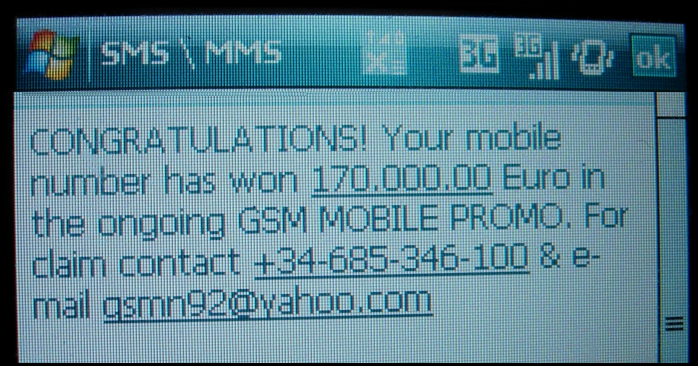
People are receiving text messages to their phones that look something like this:

CONGRATULATIONS! Your mobile number has won 170.000.00 Euro in the ongoing GSM MOBILE PROMO. For claim contact +34-685-346-100 & e-mail gsmn92@yahoo.com

If you send an e-mail to the listed address, this is what you'll get back:


From: Gsm Notification (gsmn92@yahoo.com)
Date: 11.06.2008 11:49
FROM THE
DESK OF THE PROMOTION OFFICER,
GSM MOBILE SWEEPSTAKES PROMO.
CALLE CLAUDIO COELLO 41, 28001 MADRID,
SPAIN.

UNITED KINGDOM ( UK ) / SPANISH ALLIANCE GSM SUBSCRIBERS PROMOTION.

To,
Mr. Xxxx Xxxxxxx .
Verification No: CN435-663-6
Winning No: +35840XXXXXX
Country: Finland.

Date: 11th June , 2008.

Congratulations!!! On behalf of UNITED KINGDOM(UK)/SPANISH GSM Staffs we hereby

Congratulates you on your Mobile Phone Serial Number has won you the Sum of

€170,000.00 (One Hundred and Seventy Thousand Euro) on the ongoing UNITED
KINGDOM(UK)/SPANISH GSM MOBILE PROMOTION . A Cheque has been issued under your name ( Xxxxx Xxxxxxx.) and it will be Deliver to your House Address through the Deplomate Parcel Officers.

But you will never get any parcel or any check!

Read The full story here

Do you double check the web addresses?

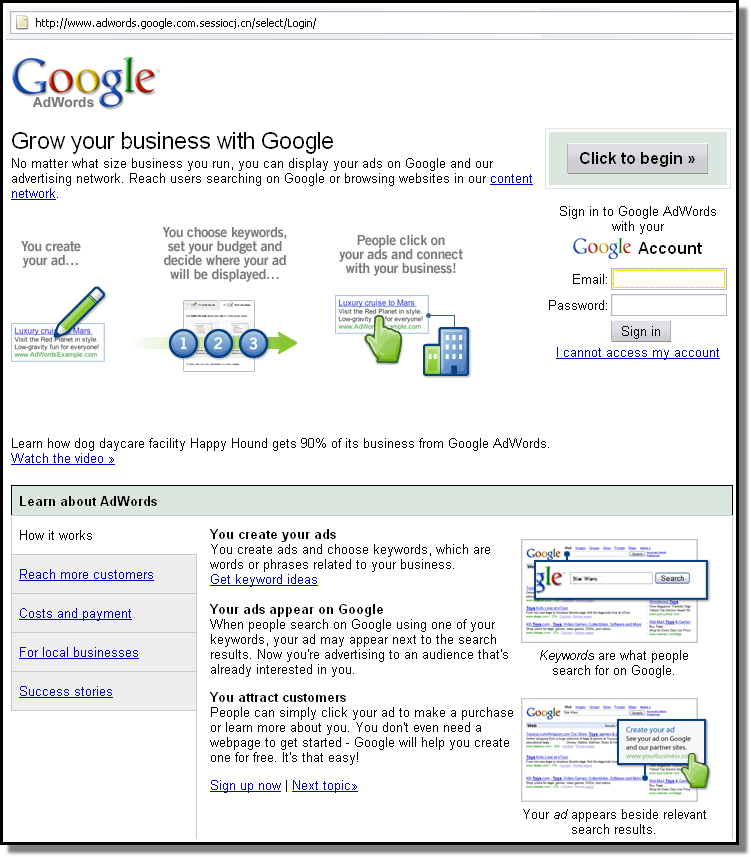
To avoid phishing, double check the web addresses. Especially, those where you need to input information about yourself.

The above picture is a screenshot of a fake phishing website, fully loaded to cheat you. But it looks more authentic than Google.

So, double check the address. And if you feel suspected, try PhishTank to verify.


Photo courtesy F-secure

Anatomy of a phishing site


Here is the anatomy of a phishing site. Discussed in great detail. brought to you by F-secure blog. You will wonder that hundreds of bogus websites containing Paypal and Citibank as words in their bogus URL had been used to fool innocent Internet users. A MUST read.

Read the complete story here:

Anatomy of a phishing site

How to avoid mobile phishing attacks


They were quite active in internet using emails and web-sites. Now they have devised a new, innovative way. Phishers have started targeting innocent mobile phone users.

From now on, you may receive SMS that may read like this

"Official Microsoft ANNOUNCEMENT: Congratulations! Your mobile phone has won US$ 10 Million prize money. To claim your money, call this number XXXXXXXX tomorrow at 8 AM. Thank you. "

Obviously, steer clear of such messages and delete them immediately. If possible, lodge a report about the phone number in nearest police station.

There is a funny incident described at F-secure blog about one such mobile phishing attack.

It looks like that phishers use - the same method - they were using for Nigerian type phishing attacks - they lure targets showing they have Won money or some huge money needs to be fixed illegally on share basis. Once the target comes in their net, they extract money in the name of completing formalities.

Tag ,,,

Windows Vista's security busted

And, that too with its own ANIMATED cursor!

Windows Vista is hyped to be a most secure Operating System till date. It has built in antivirus tool called Windows Defender.

But, what can you say when Windows Vista's security falls with its own "Animated cursor exploit" that is known to Microsoft since December 2006! The ANI exploit is a bug in the way Windows renders animated cursor files that can allow execution of arbitrary code under the privileges of the user that downloaded the malicious file. Here is an example with Video - how Windows Vista falls and crashed with this exploit.

This "ANI exploit" can effect almost all versions of Windows. There were reports that some ANI exploits are spreading fast through some hostile domain.

Microsoft has released an update about this, and a patch may be ready by this evening.

Update 1 # Zdnet had reported that more than 150 sites had already been infected and counting...

Update 2 # And now Firefox too had this flaw.

Tag ,,,

Add to your del.icio.usdel.icio.us Digg this storyDigg this

How Phishing sites work? See it live on You tube.


Yes, F-secure had brought a video for you that you can download (8 MB, XviD format) to watch how phishers work. Alternatively, you can watch the video on Youtube here.

Phishing sites registers themselves with look-alike names to fool users. In the said video, working of a phishing site named - services-paypal.com had been investigated. The phisher was found to redirect credit card information to a certain gmail mail address!

Must watch informative video.

Tag ,,,

Add to your del.icio.usdel.icio.us Digg this storyDigg this

See the Global Virus activities in real time.


Now you can see the global activities of viruss in your computer's monitor.


F-secure, the security firm had hosted a free service WorldMap Live for quite some time that shows Global activities of all kinds of virus on a world map that constantly refreshed every hour or so. The activities of viruses, their name, and their physical locations (infections and spreading) are recorded and displayed in real time. They are arranged neatly in Quite, Low, Medium, High and Epidemic scale. Beside the map, you can see the name of highly active viruses - indicating percentage infections. As it is obvious in the screenshot, currently, the Benwarum email warm is most active with total 44% resulted infections. Interestingly, variants of Mydoom and Netsky are still active and are responsible for second and third most virus infections.

According to F-Secure, WorldMap Live works this way :-

When a virus activity detection occurs, many F-secure security products report back to F-secure with data that includes an IP address. That particular IP address is converted to a physical location which is then displayed on the WorldMap. The WorldMap software runs in real-time as well as 1hour and 24hours playback mode.

You can click upon various parameters there to get detailed information. The worldmap is scalable and you can view a particular continent or a region or a country. The screenshot here shows that there were huge virus activity going on at USA and Europe countries - the area with dense PC penetration.

F-secure also offers online virus scanning for free.

Related article:

Beware of phishing scams...

Tag ,,,

Add to your del.icio.usdel.icio.us Digg this storyDigg this